If you’ve already deployed MFA across your organisation, it’s easy to assume you’re in a good place from a security perspective. A few years ago, that would probably have been true. Today, however, the threat landscape looks very different.
Microsoft has been steadily raising the security baseline across Microsoft Entra ID and Microsoft 365, and one of the most significant changes is the move towards phishing-resistant authentication becoming the default expectation rather than an advanced security feature.
Traditional MFA methods such as SMS codes, phone calls, Microsoft Authenticator prompts, and one-time passcodes have undoubtedly improved security. Unfortunately, modern attacks increasingly focus on bypassing these controls through techniques such as adversary-in-the-middle phishing, MFA fatigue, token theft, and session hijacking.
That’s why organisations are now being encouraged to move beyond simply enabling MFA and towards using authentication methods designed to resist phishing attacks altogether.
The direction of travel is clear: organisations need authentication methods that are resistant to phishing by design, not just harder for attackers to abuse.
Why Microsoft is driving this change
One advantage Microsoft has is visibility. Every day, it processes an enormous volume of authentication requests across Microsoft Entra ID and Microsoft 365, providing valuable insight into how identity-based attacks continue to evolve.
Despite years of security improvements, password-based attacks are still one of the most common ways attackers gain access to organisations’ environments. What’s more concerning is that modern phishing kits have become sophisticated enough to capture not only usernames and passwords, but also MFA responses in real time.
This highlights an important reality: while traditional MFA is significantly better than relying on passwords alone, it isn’t immune to attack. Different authentication methods can be targeted in different ways:
- SMS codes can be intercepted or obtained through social engineering techniques.
- Voice call verification can be vulnerable to telecom-related attacks and account takeover attempts.
- Push notifications can be abused through MFA fatigue campaigns, where users are bombarded with prompts until they eventually approve one.
- One-time passcodes (OTPs) can be captured by phishing proxy services that sit between the user and the legitimate sign-in page.
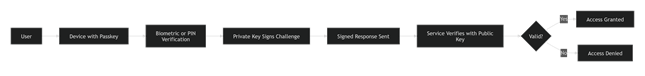
Phishing-resistant MFA takes a fundamentally different approach. Rather than relying on a code or approval that a user can be tricked into providing. Authentication is bound to the legitimate service being accessed and the device it is being accessed from.
In practical terms, this means that even if a user is lured to a convincing fake website, the authentication attempt cannot succeed. The security key, passkey, or authentication method recognises that the request is coming from the wrong domain and simply refuses to authenticate. The result is a much stronger defence against modern phishing attacks and one of the key reasons Microsoft is increasingly positioning phishing-resistant authentication as the future of secure sign-ins.
The Three Main Options for Phishing-Resistant Authentication
When organisations start exploring phishing-resistant authentication, they typically encounter three technologies that are now widely recognised as the leading options: passkeys, FIDO2 security keys, and Windows Hello for Business.
While each works slightly differently, they all share a common goal: replacing credentials that can be stolen, intercepted, or tricked out of users with cryptographic authentication methods that are far more difficult for attackers to compromise.
| Passkeys | FIDO2 Security Keys | Windows Hello |
| Passwordless | Hardware-backed | Device-bound |
| Easy user experience | Highest assurance | Native Windows |
| Growing adoption | Great for privileged users | Ideal for Windows fleets |
Passkeys
Passkeys are rapidly becoming one of the most talked-about developments in identity security. Rather than relying on a password that a user must remember and enter, passkeys use cryptographic key pairs to verify identity securely behind the scenes.
From a user perspective, the experience is simple. Authentication can often be completed using a fingerprint, facial recognition, device PIN, or another trusted sign-in method already available on the device.
One of the biggest advantages is that there is no password to steal and no code to enter into a fake website. Authentication is linked to the genuine service being accessed, making traditional phishing attacks significantly less effective. As a result, passkeys are increasingly being adopted across consumer and enterprise platforms, including Microsoft Entra ID.
FIDO2 Security Keys
For organisations seeking a dedicated hardware-based solution, FIDO2 security keys remain among the strongest authentication options available.
These small physical devices, such as those produced by YubiKey, Feitian, and Token2, allow users to authenticate by inserting or tapping the security key when signing in. The authentication process is backed by cryptographic protections stored within the device itself, removing the need for passwords and reducing the risk of credential theft.
The appeal of security keys is their simplicity. Users gain a fast and consistent sign-in experience, while security teams benefit from an authentication method that is highly resistant to phishing, credential harvesting, and account takeover attempts.
Windows Hello for Business
Windows Hello for Business takes a similar cryptographic approach but integrates it directly into the Windows sign-in experience.
Instead of entering a password, users authenticate using a PIN, fingerprint, or facial recognition. Behind the scenes, Windows uses a securely stored credential that is tied to both the user and the device.
This means the authentication process is not dependent on a reusable password that could be captured and reused by an attacker. Because the credential remains protected on the endpoint and is designed to validate against legitimate services, it provides strong protection against many common identity-based attacks while also improving the everyday user experience.
Preparing for Phishing-Resistant MFA
Assess your current MFA estate
Before moving to phishing-resistant authentication, you need to start by understanding what you already have. This gives you a realistic view of where risk exists and where change will have the biggest impact.
Useful questions include:
- Which MFA methods are currently in use?
- How many users still rely on SMS authentication?
- Are voice calls still enabled for verification?
- How many users have Microsoft Authenticator configured?
- Are privileged accounts already using stronger authentication methods?
- Are break-glass accounts properly secured?
Microsoft Entra reporting can help identify the authentication methods users have registered. Pay particular attention to Global Administrators, Privileged Role Administrators, Security Administrators, Helpdesk Administrators, and executive leadership teams. These groups should be prioritised first.
Review your Conditional Access policies
Conditional Access will be central to enforcing stronger authentication requirements. The key is to move beyond simply asking whether MFA was used and start asking which type of MFA was used.
Authentication Strengths in Microsoft Entra ID are especially useful here because they allow organisations to require specific phishing-resistant methods, such as FIDO2 security keys, Windows Hello for Business, or passkey authentication.
This gives you a practical way to phase in the transition rather than forcing a disruptive, organisation-wide change overnight.
Start with administrators
Privileged identities should be the first priority. They are high-value targets, and securing them early delivers immediate risk reduction while giving IT and support teams experience with the new authentication methods.
A sensible rollout path could look like this:
- Enable phishing-resistant MFA for Global Administrators.
- Extend the requirement to all privileged roles.
- Roll it out to IT staff.
- Expand to high-risk users.
- Move gradually to the wider employee population.
This staged approach keeps the rollout manageable while still making progress.
Prepare your end users
The technology is only one part of the change. Users need to understand why authentication is changing, what passkeys are, how Windows Hello for Business works, how security keys are used, and what they should do if a device is lost or replaced.
Good communication should include awareness messaging, simple user guides, short training videos, self-service registration instructions, and clear support escalation paths.
A better user experience is possible: once people are familiar with the process, phishing-resistant authentication can often feel easier and smoother than traditional MFA.
Validate device readiness
A successful rollout depends on knowing whether your devices are ready. Review Windows versions, Intune management status, TPM availability, biometric hardware support, and mobile device readiness.
For Windows Hello for Business, confirm endpoints meet Microsoft’s recommended hardware and configuration requirements. For passkeys, check support across the mobile platforms your users rely on.
Develop a recovery strategy
Recovery is one of the most important — and most overlooked — parts of a phishing-resistant authentication programme. Strong authentication is only successful if users can recover safely when something goes wrong.
Plan for common scenarios such as lost security keys, replaced mobile devices, damaged laptops, and emergency access requirements.
Good practice includes registering multiple authentication methods, issuing backup security keys for privileged users, maintaining monitored break-glass accounts, and documenting recovery procedures. A strong recovery process prevents security improvements from becoming operational blockers.
Monitor adoption and usage
Migration should be measured continuously. Track authentication method registrations, passkey adoption, FIDO2 usage, authentication failures, Conditional Access policy impact, and helpdesk ticket volumes.
Microsoft Entra reporting and log analytics can help highlight adoption trends and identify where users may need extra support.